Security & trust
Let AI agents do real client work—without handing over your credentials.
Outloop is a local-first access layer for teams running AI agents across many client systems. Agents work through connections you approve, and the normal brokered API flow does not return raw credential values to the agent.
- Agents work through connections you approve
- Brokered API access does not return raw credentials
- You grant, review, and remove access at any time
Last updated:
In short
Normal brokered API access lets agents use approved client systems without receiving raw credentials.
Access is configured per Workspace and connected system. Known-secret and sensitive-pattern redaction applies to returned results; business data can remain sensitive. Review the data-flow and isolation pages for optional Cloud paths, host-access limitations and what removing access does—and does not—revoke.
Real work, not a read-only demo
Outloop does not reduce every connection to a read-only demo. Agents can do the work the job actually needs, inside the access you approved.
Security is the control layer. The outcome is running more client workflows without rebuilding access every time.
How it works, at a high level
-
Your agent
Asks Outloop to do something in a client system.
-
Outloop-controlled access
Uses the connection you approved for that workspace.
-
Customer-approved service
The system you connected, through its official API.
What Outloop controls
-
Approved connections, not shared secrets
Agents work through connections you approve. The normal brokered API flow does not return raw credential values to the agent. Host compromise and separately configured integrations have different boundaries.
-
Scoped per workspace and per system
Access is controlled for each client workspace and each connected system. A new workspace starts with no access until you grant it.
-
Permissions you choose
Connections use each provider’s official API and OAuth flows. You decide which permissions and administrative consent to grant.
-
Recorded activity, redacted output
Local activity is recorded and known secrets and sensitive patterns are redacted. Business data, images and other outputs can still be sensitive.
The enforcement boundary, recorded
Resource restrictions apply to supported, configured connector operations. In this demo workspace, requests for an account or Meta object outside the workspace’s binding were refused, while approved requests kept executing.
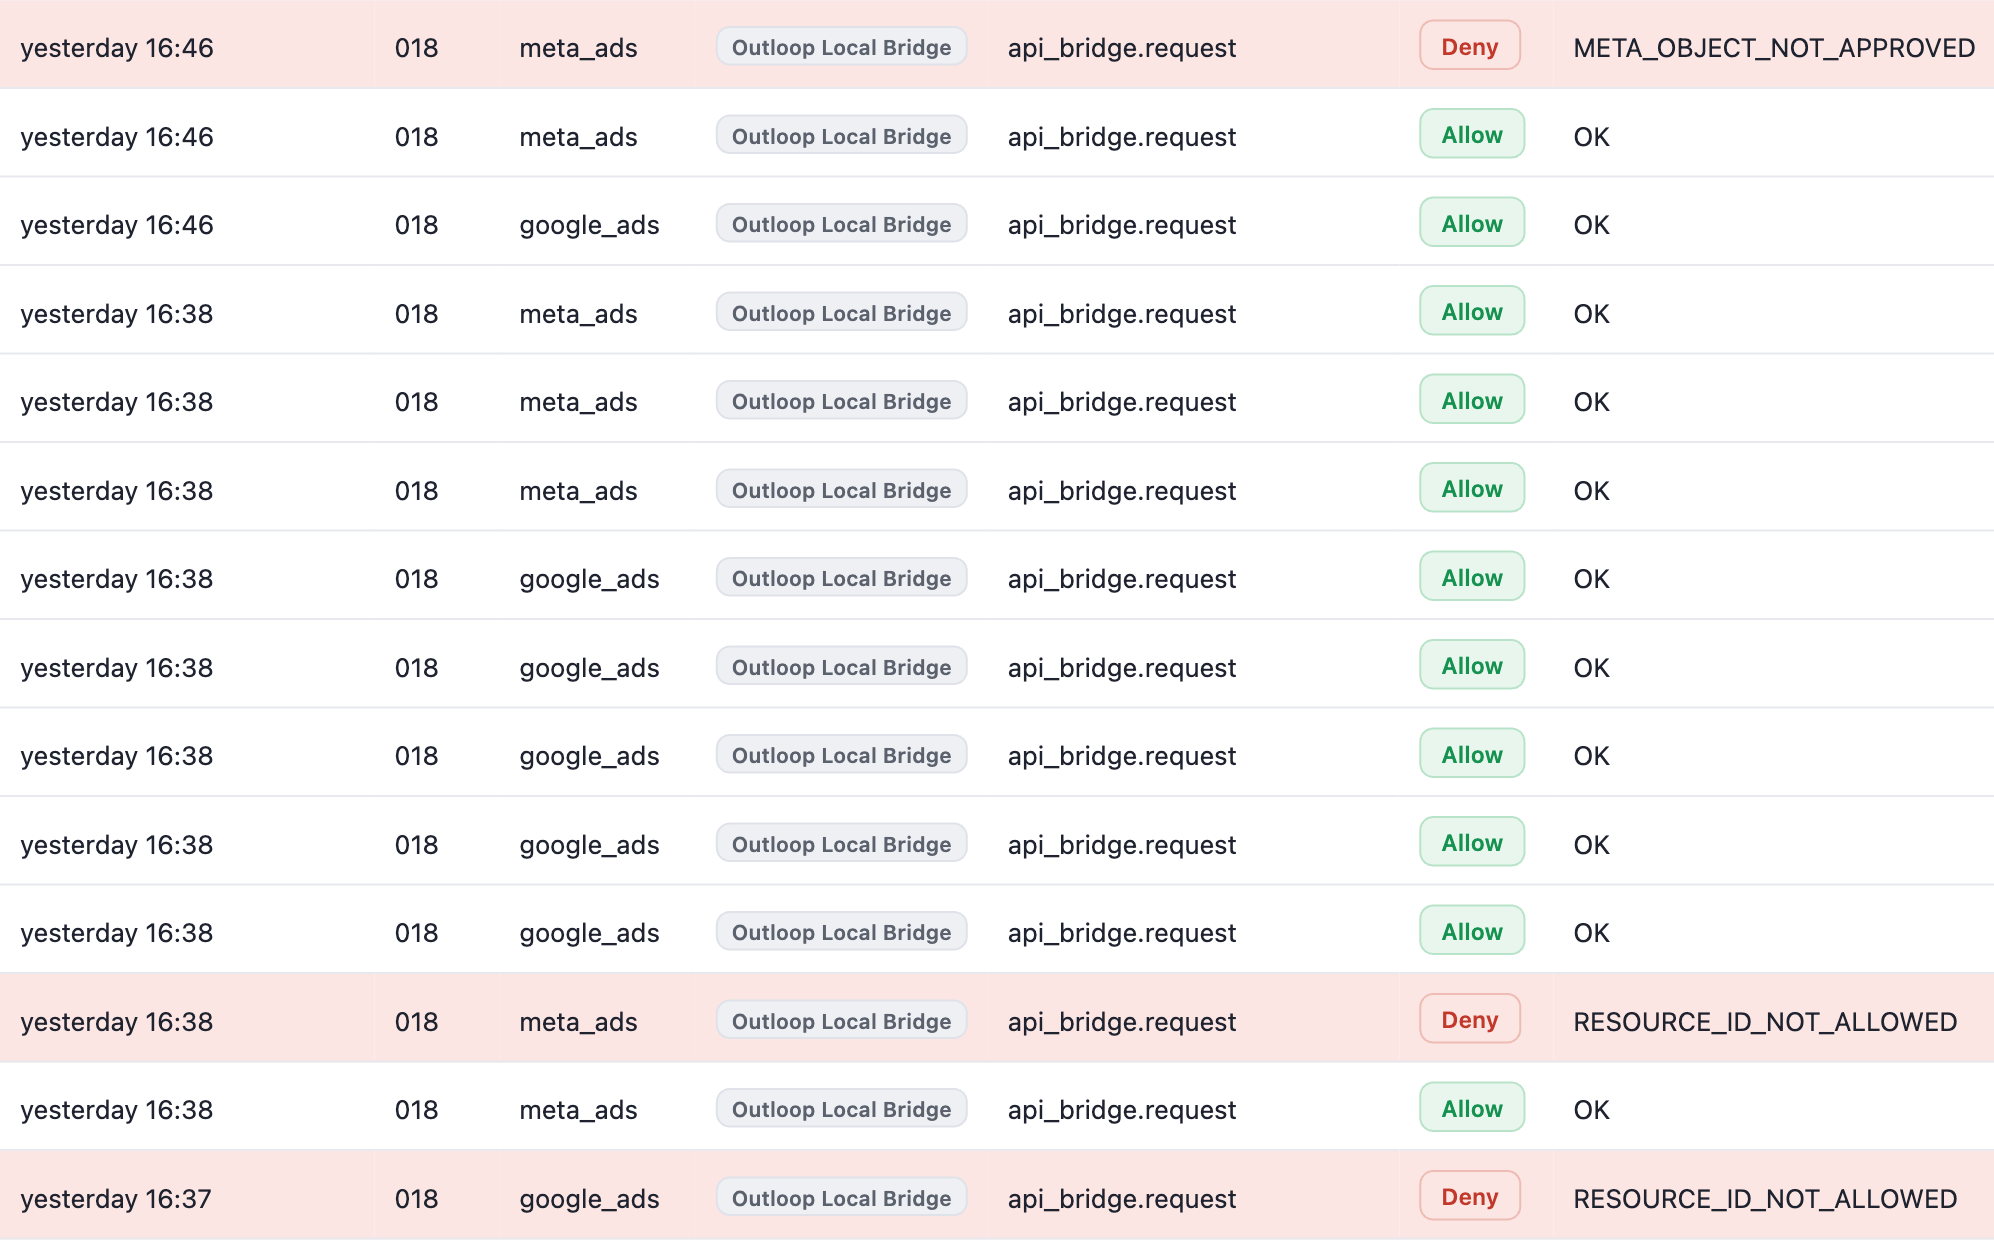
Swipe sideways to read the log · open full size
Refused: these wrong-resource requests did not run
- Deny ·
RESOURCE_ID_NOT_ALLOWED(google_ads and meta_ads) — the request named an account outside this Workspace’s approved resources; the requested action was refused - Deny ·
META_OBJECT_NOT_APPROVED(meta_ads) — a campaign, ad set or ad that does not belong to the approved ad account; the requested action is not sent to Meta - Approved requests in the same workspace keep executing around the refusals — Allow · OK
Real execution in an Outloop demo workspace (workspace 018), published in the September 26, 2026 proof pack — not a customer case study, and not evidence of ad spend, delivery or performance. Enforcement covers requests routed through Outloop. See the runtime access walkthrough for the recorded flow.
Where each kind of data is handled
| Data | Where it is handled | Outloop Cloud | Agent visibility |
|---|---|---|---|
| Raw API credentials and OAuth tokens | macOS Keychain for normal brokered API access | Feature-specific OAuth transit / encrypted transfer exceptions | Not returned by the normal brokered API flow |
| Work done through an approved connection | Your Mac and the approved provider; your agent may also send content to its model | Ordinary API traffic goes directly to the provider; optional feature paths differ | Results processed for redaction; business data can remain sensitive |
| Activity records | Local activity audit on your Mac | Separate Cloud operational records may exist | Local activity views; not a complete or immutable audit guarantee |
| Account, trial, billing, licensing, onboarding, activation | Outloop Cloud | Service metadata only | No customer API credentials |
| Workspace and access identifiers | Where required for identity, entitlement and configured features | Identifiers, states and limited operational metadata | No raw credential retrieval through the brokered API flow |
Feature-specific processing is described in the data-flow overview. The published policy for website, account and billing data is in the privacy policy.
You stay in control
Nothing grants itself access. A person decides what each client workspace can reach, and can withdraw it at any time.
- Choose which systems each client workspace can reach
- Choose the permissions each connection is granted
- Review activity for a workspace
- Remove access at any time, without ever handling the credential
A read-only connection is a safe way to start. Broader access is granted only when you decide to grant it.
Connecting to the systems you already use
Outloop connects through official provider APIs and OAuth flows where applicable. You control the permissions and administrative consent granted by each provider.
Which systems are connected, and what each one may do, is set per client workspace. The published setup guides cover the services we have documented.
Outloop works alongside your password manager
Outloop is not a replacement for a password manager or vault. It adds the layer you need when AI agents — not people — are doing the work: approved access per client, recorded activity, and redacted output.
More on that boundary: Outloop is not a vault.
Build integrity and current limits
The Outloop Mac app is signed with an Apple Developer ID, runs under the hardened runtime, and is notarized and stapled by Apple, so macOS Gatekeeper accepts it as a notarized Developer ID application.
Outloop is an actively developed product available with setup guides and product support. Do not treat it as independently certified security infrastructure. Here is what we do not claim:
- This page does not claim SOC 2 or ISO 27001 certification, or GDPR/HIPAA compliance
- This page does not claim completed independent penetration testing
- This page does not claim enterprise SSO or SCIM provisioning
- No published breach-response SLA and no data-residency guarantee
- No immunity to prompt injection, and no claim of complete prevention of every possible wrong-client action
Review the linked Trust Center pages for qualifications and feature-specific data flows. We would rather answer a questionnaire honestly than publish a badge we have not earned.
Preparing a formal security review?
We respond directly to security questionnaires based on current, verified product behavior. Additional detail is shared with qualified reviewers on a need-to-know basis, and deeper material is provided under NDA where appropriate.
Book a security walkthroughResponsible use
Outloop is intended only for API credentials, accounts, workspaces, systems, and data that you own, manage, or are legally authorized to access. It must not be used for unauthorized access, credential theft, spyware, keylogging, account takeover, spam, abuse, or unlawful activity.
Security contact and disclosure
For security questions or responsible disclosure, contact
support@outloop.co.
Please do not include raw API keys, passwords, bearer tokens, authorization headers,
.env contents,
or customer secrets in your report.
Questions reviewers ask first
Give agents the access they need—without giving them the credentials.
Create your trial. Download the Mac app. Run your first approved connection.